Program analysis
 Agentic security
 Paper
 Code
 PDF



Johns Hopkins University
PhD, Computer Science · Expected Dec 2027
Computer Science PhD candidate
Johns Hopkins University
Advisor: Yinzhi Cao
CoBrA · ICSE 2026FAST · IEEE S&P 2023AnonVul · Preprint 2026
PHP applications can choose which functions to call at runtime, making vulnerabilities difficult to detect statically. I designed and built CoBrA to resolve these calls using their calling context and track unsafe input flows. It found 54 previously unknown vulnerabilities in 19 web applications.
 Which paths can this request take?
PHP
Dependencies within controller
$action . "_controller" → ?
Adapted from the paper’s Emoncms example; parsing, database setup and the other engine’s body are omitted. Predefined analysis states; no PHP or CoBrA execution.
FAST addresses the cost of analyzing dynamic JavaScript by constructing candidate call paths, then focusing analysis on statements relevant to a potential vulnerability. I implemented JavaScript abstract interpretation and led the evaluation, which found 242 previously unknown vulnerabilities in npm packages.
AnonVul evaluates whether vulnerability-discovery agents find business-logic flaws or rely on recognizable software identity. The benchmark uses anonymized vulnerability tasks, sandboxed execution and expert-defined checks to test discovery performance.
3R-Bench tests how preceding conversation changes an LLM’s response to the same cybersecurity request. It distinguishes refusal, bounded assistance, compliance and provider blocking, separating response behavior from the request itself.
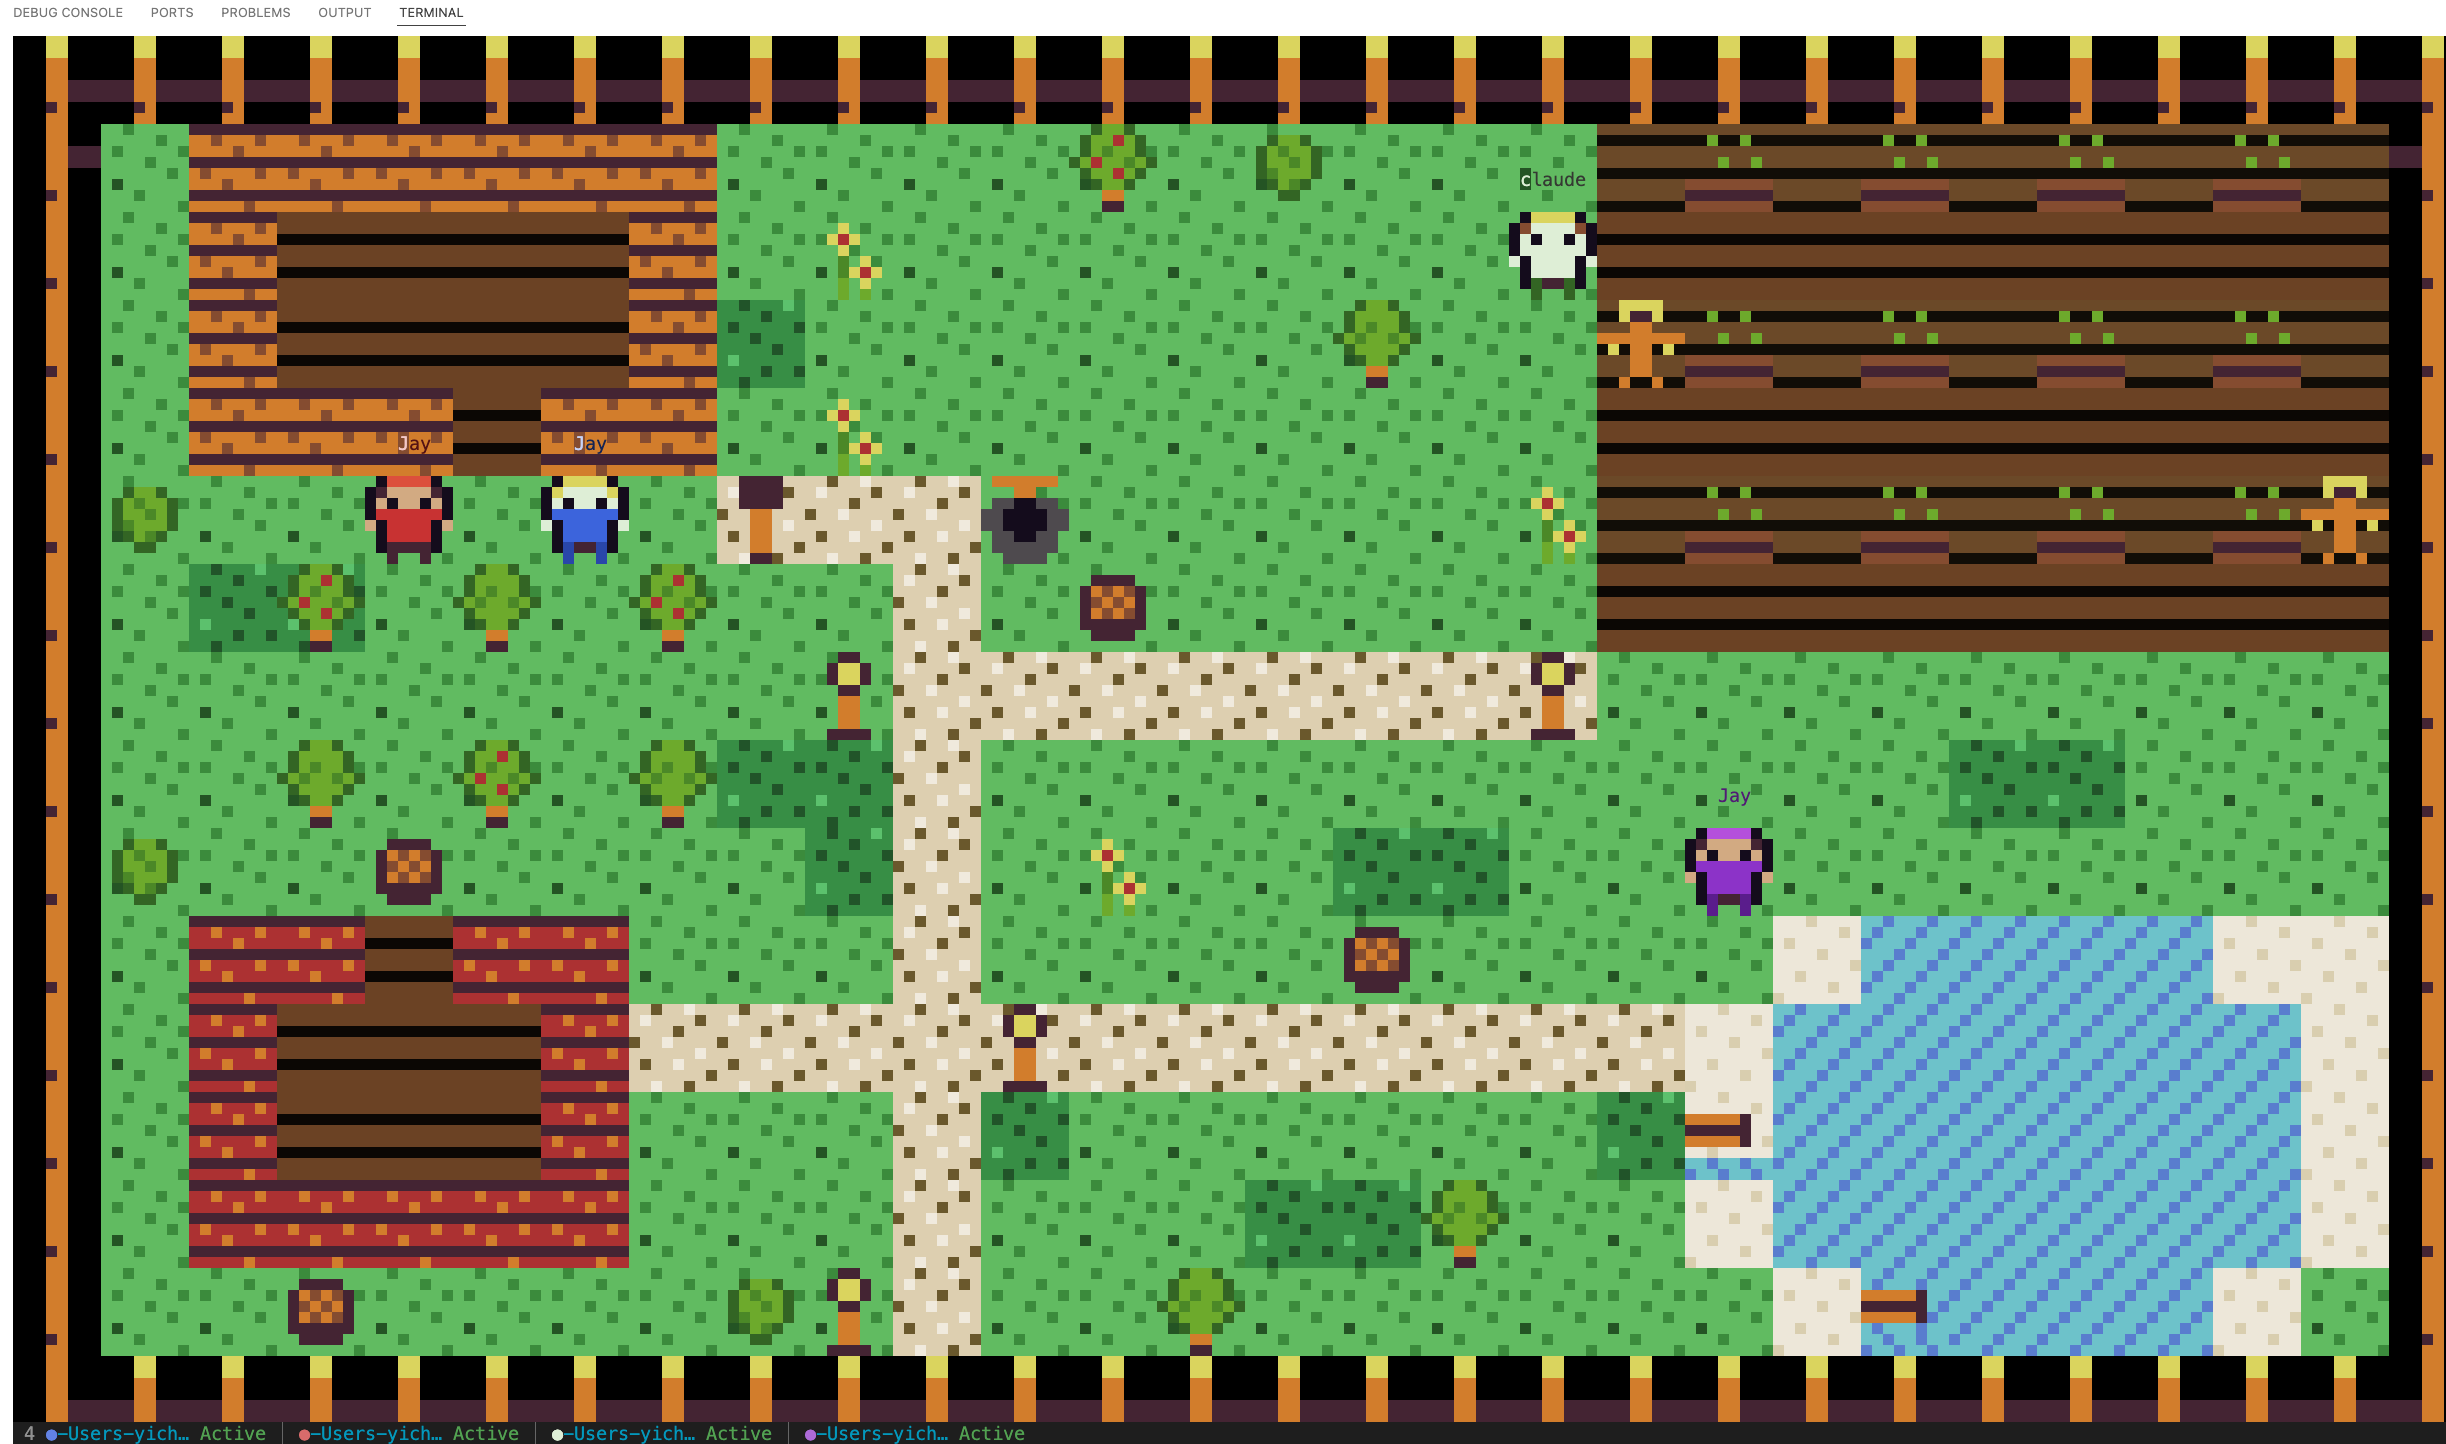
Monitoring Claude Code sessions through animated farm characters in a terminal dashboard
CodeRustShows when agents are working, idle or waiting for input.
Requires Rust 1.85+ and a terminal with 24-bit color.
git clone https://github.com/samhsu-dev/harvest-claude.git
cd harvest-claude
cargo install --path .
harvest-claude
Active Claude Code sessions appear automatically as farm characters.
Extending PHP security analysis with five vulnerability queries, regression tests and version-check fixes
CodeScalaPR #5327 · mergedContributed upstream queries for SQL injection, command injection, code injection, unsafe file operations and XSS, with positive and negative tests. Also fixed PHP version checks for distribution-specific version strings. PR #5327 was merged on February 28, 2025.
A minimal SQL-injection case from the merged PR’s tests:
<?php
$input = $_GET["username"];
$query = "SELECT * FROM users WHERE name = '$input'";
$result = mysql_query($query);
The contributed query checks whether request input reaches a database call. The test pairs this case with a constant-input case that should produce no match.
Querying Joern code property graphs in Python to explore program structure and data-flow relationships
CodePythonSupports loading exported graphs, querying nodes and edges, and traversing their relationships.
Install with pip install cpg2py. Use tab-delimited nodes.csv and rels.csv exports.
from pathlib import Path
from cpg2py import cpg_graph

graph = cpg_graph(Path("nodes.csv"), Path("rels.csv"))
for node in graph.nodes(lambda n: n.type == "Function"):
    print(node.name)
Prints the function names in the supplied graph.
Adapting the legacy RIPS PHP analyzer for command-line scanning and structured JSON reports
CodePHPAdapted RIPS v0.5 to run without its web interface, adding command-line options and JSON reporting for automated analysis workflows. Uses the original, discontinued RIPS v0.5 analysis engine.
Requires PHP. Replace /path/to/php/project with a local PHP source directory.
git clone https://github.com/samhsu-dev/ripsv0.5-cli.git
cd ripsv0.5-cli
php rips.php /path/to/php/project --vector=xss --format=json
Scans the source for potential XSS and prints the findings in JSON format.
Jan 2023 – Present
PhD, Computer Science · Expected Dec 2027
Sep 2021 – Dec 2022
MS, Security Informatics
Sep 2019 – Oct 2020
MSc, Software Systems Engineering · Distinction
2015–2019
BSc (Honours), Information and Computing Science
Feb 2026 – Present
Maintained 8 agentic pipelines for software vulnerability discovery. Developed 1 black-box analysis pipeline and 2 dynamic analysis pipelines.
Dec 2020 – Mar 2021
Designed a Hyperledger Fabric framework for product traceability, with access controls for business-sensitive records.
Sep 2021 – Present
Research on software vulnerability discovery through static analysis and fuzzing.
Sep 2022 – 2023
Built C++ simulations in OMNeT++ to study denial-of-service attacks and defenses in vehicular networks.
Jun–Sep 2020
Built a Python tool to link tests to source methods using their co-evolution in Git repositories.
2025
Teaching Assistant (TA) · Johns Hopkins University
2023
Teaching Assistant (TA) · Johns Hopkins University
2022
Course Assistant (CA) · Johns Hopkins University
Jul 2018
Outstanding Achievement